

Who Signed That Purchase Order?
Why AI-Era Procurement Needs a New Delegation of Authority — Not a New Platform
Executive Opening
A delegation-of-authority (DoA) matrix outlines what an employee may buy; how far they can go on their own, when an exception needs approval from a manager and when there was authorization for the transaction with which a person has committed capital (an auditor will know this too).
An AI agent can now select a contracted supplier and release a purchase order without a human approving that transaction. The order may be compliant. But who authorized the agent to commit capital, who controls its cumulative exposure, and who can withdraw that authority?
Trinity believes that the solution to this problem does not involve another platform, nor do we believe it involves another framework. Rather, an extension of the existing DoA for the enterprise itself by way of the Ownership Test™ and Action Ownership Register explained in Trinity Insights Series #010.
The Problem Today: Access Is Not Authority
In a Gartner study with 101 CPOs from January–February 2026, only 36% reported being “very” confident that they could redesign job responsibilities and processes to support the use of AI. The data reflects the CPO’s confidence in the organization’s design of work — not failures by procurement personnel to follow established controls. In separate guidance issued to boards in 2026, KPMG also stressed the governance of delegating responsibility and oversight of financial reporting when agents complete transactions.
For CFOs and CPOs, three distinctions matter. Technical permission determines what an agent can execute. Commercial authority defines which commitments it may make. Continuing accountability identifies who monitors the consequences and can intervene.
Configuring the first does not establish the other two.
What is changing: compliance may conceal exposure
Compliance with all thresholds for each individual purchase order does not guarantee that total commitment will not exceed the intended budget, inventory requirement, or supplier concentration limit.
Illustrative exposure — $2.5 million
Consider a hypothetical purchasing agent who has been granted permission to enter purchase orders up to $5,000. In this example, with 500 such entries for orders totaling $2.5 million, each entry may be within their individual authority to approve while collectively exceeding the total amount of risk that the company had planned for.
The control failure is not unauthorized execution. It is insufficient control over cumulative commercial authority.
PwC describes 87 cases in a cross-platform agent scenario where commissions exceeded deal margins after third-party costs. This is not a procurement benchmark; it illustrates how individually authorized actions can combine into financial exposure that no single system detects.
The control boundary must follow the commercial commitment across systems, not stop at the approval screen.
The Stronger Alternative: An Agent-Aware DoA
The existing approval matrix should be extended, not replaced.
| Dimension | Traditional DoA | Agent-aware extension |
|---|---|---|
| Authority | Human approver | Identified agent, permitted action, named owner |
| Scope | Category and order value | Supplier, contract, exceptions and business conditions |
| Exposure | Per-order limit | Per-order and cumulative commitments |
| Evidence | Approval record | End-to-end authorization and execution trail |
| Duration | Standing delegation | Review, recertification, suspension and revocation |
Source: Trinity Solutions Global analysis
This is a practical application of Series #010's Ownership Test™, not a new proprietary method. All grants recorded on the Action Ownership Register must include an identified leader that has the ability to:
- See it: Trace the decision, order, and aggregate exposure.
- Shape it: Adjust suppliers, limits, and escalation conditions.
- Answer for it: Explain authorization and financial consequences.
- Stop it: Suspend or revoke delegated purchasing authority.
Business ownership complements finance controls, segregation of duties, and independent audit; it does not replace them.
Operating Model Impact: From Planning to Enterprise Value
ASCM's SCOR Digital Standard places all of an organization's business rules, contracts, enterprise-wide planning, risk management and compliance within Orchestrate. NIST's February 2026 draft concept paper addresses Agent Identity, Authorization, and Auditing. Neither of these standards provides the DoA extension prescribed by Trinity.
A purchasing authority must maintain connectivity with changes in customer demand, inventory levels, suppliers' risk profiles and the company's cash flow. A contract-compliant order can undermine enterprise value when planning conditions shift.
Series #011's promise-to-cash argument therefore extends to the authority to spend:
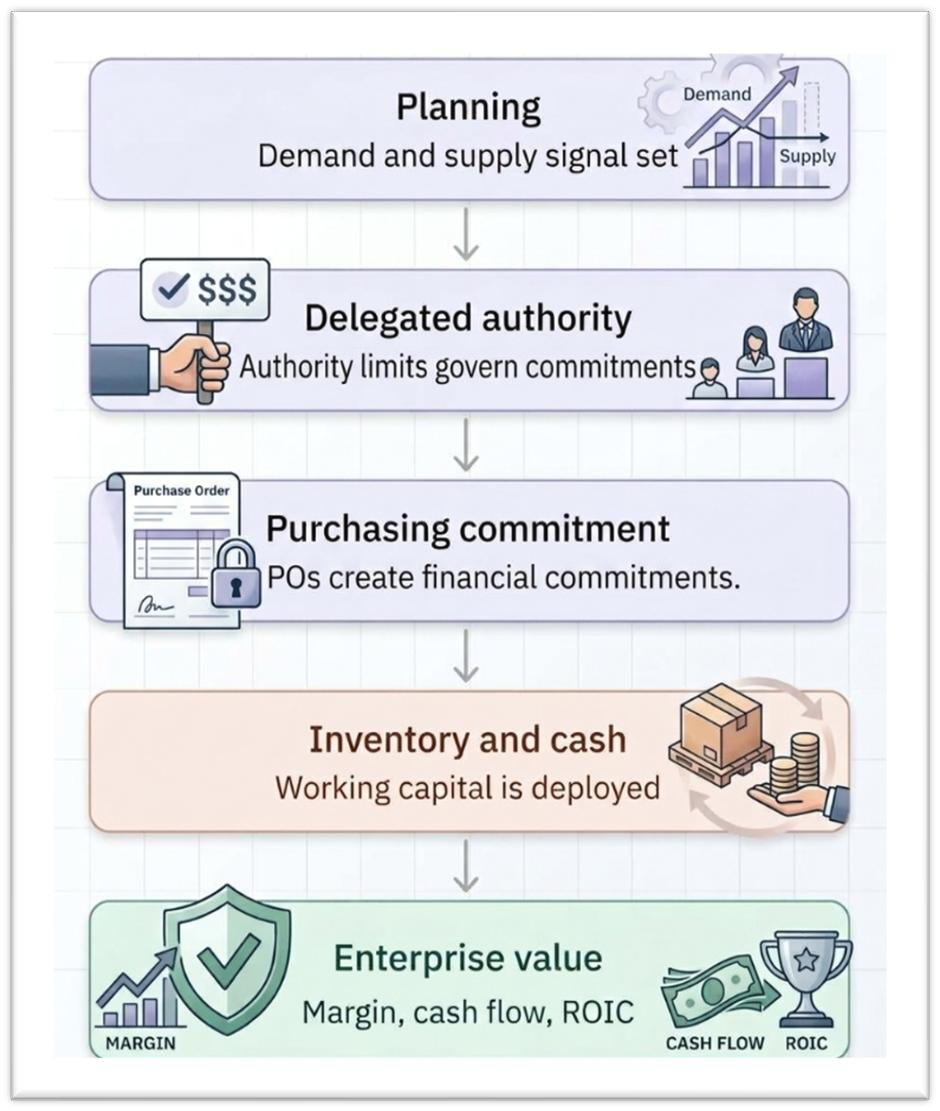
Over the next 3-5 years, companies will need to begin transitioning their current "periodic" model of obtaining users' consent through an "exposure aware", "continuously monitored" model of authority.
Trinity's position on this issue is based on strategy, and NOT based on predictions made in the referenced research.
Access is not authority. AI agents may execute purchasing actions, but commercial authority must remain bounded, accountable, exposure-aware, and revocable. Trinity’s position is to extend existing Delegation of Authority—not replace it—to govern autonomous purchasing.
Strategic Actions for CFOs, CPOs, & Boards
- Identify Existing Authority. Create a list of all agents that can create, modify, or release commercial obligations (e.g. commitments) within your company, including those created internally (business-created agents).
- Extend The Approval Matrix. Register each authority grant with its owner, permitted actions, cumulative limits, exceptions, and review date.
- Establish End-To-End Accountability. Validate whether cross-system transactions are able to be recreated/reproduced/verified, whether you have the ability to see cumulative exposures, and if there is a way to immediately revoke any granted authority.
- Make Autonomy Conditional. Start with bounded and contract-based purchasing processes. Only expand the scope of authority once you have seen valid operating evidence (as validated by procurement, finance, etc.) that supports expanding the level of authority being granted.
The CFO needs visibility over committed capital; the CPO retains accountability for commercial policy and delegated purchasing decisions; and the board requires assurance that material authority remains identifiable and revocable.
Closing Insight
Approval matrices do not go away. Their assumption about actors as humans is limited.
The decisive question is no longer merely who approved a purchase order. It is who granted the authority to act, how cumulative commitments are controlled, and who remains accountable for the outcome.
The Ownership Test™ establishes that accountability. The Action Ownership Register makes it explicit. The agent-aware DoA embeds it into procurement execution.
Autonomy must be earned, bounded, monitored, and revocable.
That is how AI-enabled procurement advances from transaction efficiency to enterprise value.
Series Connection: Trinity Insights
| # | Trinity Insight | Topic / Framework |
|---|---|---|
| 001 | The Trinity Pyramid™ | Introduction to the five-layer Trinity Pyramid — from Digital Trust to Strategic Optimization. Read → |
| 002 | From Planning to Orchestration | The ADAPTIVE™ Model — eight interconnected layers for a new planning operating model. Read → |
| 003 | Digital Trust Foundation | The TRUST™ Framework — governed data, secure integration, and AI-readiness at Layer 1. Read → |
| 004 | Workflow Automation Imperative | DARE™ Framework — AI-enabled supply chain transformation. Read → |
| 005 | Human-Led AI Planning | The GUIDE™ Framework — Trinity's operating model for Human-Led AI Planning. Read → |
| 006 | Enterprise Decision Orchestration | The ORCHEST™ Framework — cross-functional decision alignment and the Decision Cockpit. Read → |
| 007 | Strategic Optimization Architecture | The APEX™ Framework — enterprise outcome optimization above orchestration. Read → |
| 008 | The Next Kodak Is Not A Technology Company | Why Governance — Not AI Adoption — Will Decide the Next Generation of Enterprise Winners. Read → |
| 009 | Leadership Lessons for the AI Era | What Satya Nadella Teaches Supply Chain and Enterprise Leaders About Governing AI Without Ego. Read → |
| 010 | From Systems of Decision to Systems of Action | The Ownership Test™ — who owns an autonomous action when no human chose it. Read → |
| 011 | From Customer Promise to Cash | The Five Stages of the Promise-to-Cash Flow — who owns the distance from commitment to cash. Read → |
| 012 | Who Signed That Purchase Order? | The Agent-Aware Delegation of Authority — applying the Ownership Test™ and Action Ownership Register to autonomous purchasing. Current paper. |
Work With Trinity Solutions LLC
Trinity Solutions LLC helps enterprises move from systems of decision to systems of action — inventorying where AI already executes, running the Ownership Test™ across every action class, and standing up the Action Ownership Register as a board-level discipline. Every engagement begins with human judgment and ends with enterprise resilience.
trinitysolutionsglobal.com | Human-Led. AI-Assisted. Wisdom-Driven.
References
- Gartner (2026). Survey Shows Just 36% of CPOs Are Very Confident in Ability to Redesign Function for AI.
- KPMG (2026). Agentic AI: Board Oversight in a New Era.
- PwC (2026). Where Agentic AI Breaks Enterprise Controls and How to Close the Gap.
- NIST NCCoE (2026). Accelerating the Adoption of Software and AI Agent Identity and Authorization. Draft concept paper.
- ASCM. SCOR Digital Standard.
- Trinity Insights Series #010 (2026). From Systems of Decision to Systems of Action.
- Trinity Insights Series #011 (2026). From Customer Promise to Cash.